# n8n SSO Pricing: Which Plans Include It (2026)
By Aisha Okoye · 2026-10-16 · Source: https://www.activepieces.com/blog/n8n-sso-pricing-which-plans-include-it-2026
---
If you want your team to log in to n8n through your company identity provider, n8n's own documentation puts that outside the free Community edition, and teams weighing open-source alternatives such as [Activepieces](https://www.activepieces.com) will want to check how each handles it.
As of 16 October 2026, you need a paid edition to get it.
Check n8n's pricing and docs pages before you commit, because edition lines move.
## n8n SSO availability by edition
### What single sign-on means for an n8n instance
Instead of keeping separate n8n passwords, people authenticate once at the identity provider, the system that holds your staff directory. In practice, a new hire gets access when IT adds them, and a leaver loses it when IT removes them.
Without it, someone eventually finds a shared login on a sticky note, and nobody can say who changed the workflow that broke invoicing at 2am.
### The five criteria every edition is judged on
Before you open a pricing page, you can answer each question below from your own setup, so you know what you're shopping for.
- Protocols. Does your identity provider speak SAML, OIDC or LDAP, and does the edition support that one?
- Cost. What does the edition that includes SSO cost for your team, and is that more than the problem is worth?
- Hosting model. Are you on n8n's cloud or running it yourself, and is SSO offered in that model?
- User and project limits. Will your headcount and the number of separate projects fit inside the edition's caps?
- Audit and admin controls. Can you see who did what, and can an admin control access by role, if an auditor asks?
However good an edition looks on the others, a mismatch on any one of these can rule it out. The next sections take the editions through this list in turn.
## How SAML, OIDC and LDAP work inside n8n
Whichever method you pick, the "who is this person" question goes to a system your company already runs. n8n then decides what that person may do, so the edition you buy only gets you the switch, not the directory work behind it.
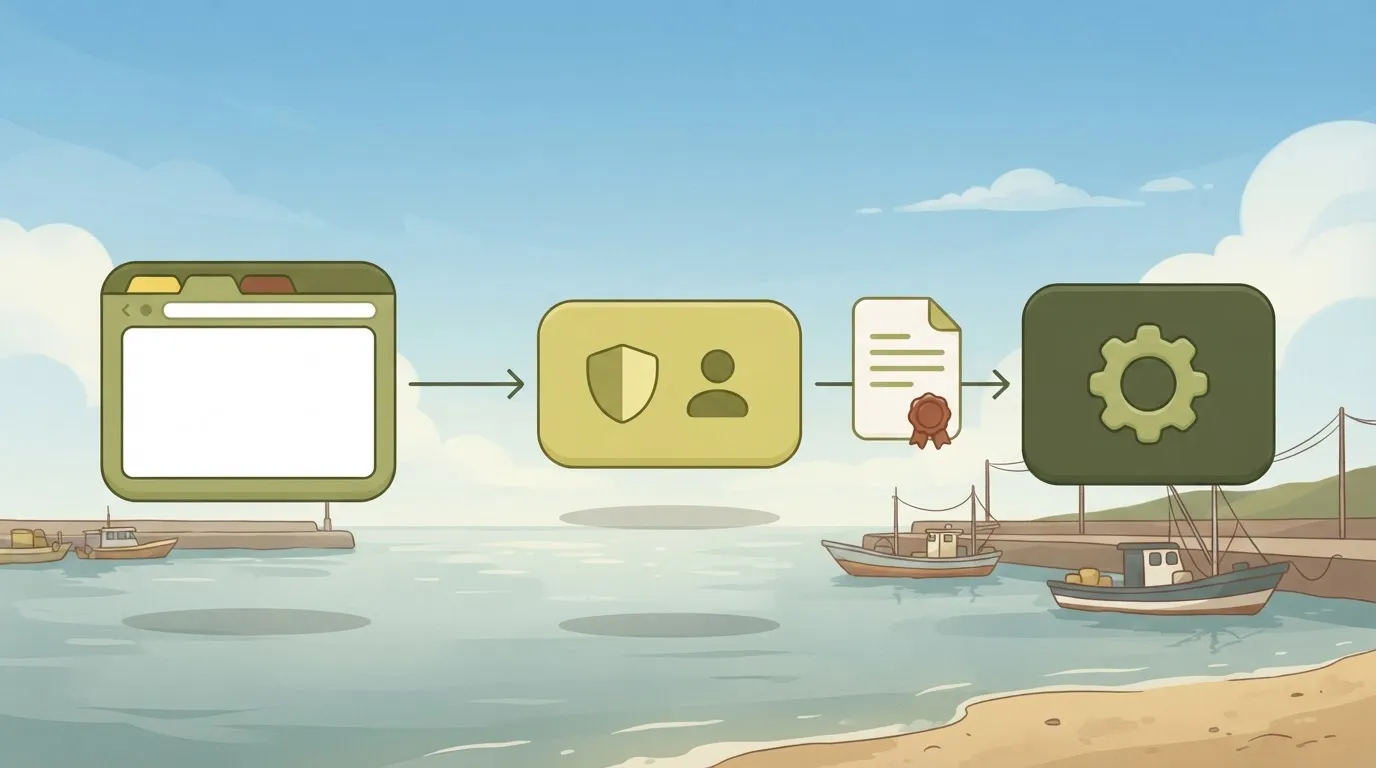
Read it for the direction of each arrow, because that's what tells you which side your IT person has to configure.
*(The illustration sits here: three lanes for the browser, the identity provider (Okta, Entra ID, Google Workspace) and n8n, with a redirect out, an assertion or token back, and an account created on first login; and a separate LDAP lane where n8n queries a directory.)*
Each method below follows from that picture. Check the exact settings on n8n's own docs before you commit, since menu names and supported providers change between releases.
### Setting up SAML login for n8n SSO
n8n sends the browser to your identity provider, the provider signs the user in and returns a signed assertion, and n8n trusts it. You configure it in n8n's SSO settings, and you create a matching SAML application in the provider.
If your team lives in Okta or Entra ID, this is usually the path with the most documentation behind it, because both are common SAML providers. Google Workspace can also issue SAML apps.
### OpenID Connect
The flow is the same shape, but the identity provider returns a token instead of an XML assertion. Setup means registering n8n as a client in the provider and pasting its client ID, secret and discovery URL into n8n.
Pick this one if your provider's admins find OIDC easier to manage than SAML certificates, and confirm it's offered on your edition.
LDAP has no browser redirect at all. The user types credentials into n8n, and n8n queries your directory server, such as Active Directory, to check them.
That means n8n must be able to reach the directory over your network, which matters for self-hosted teams behind a firewall.
With the redirect methods, n8n creates the account the first time someone signs in successfully. So nobody needs to be invited by hand, but someone does need to decide what role that new person starts with.
Check n8n's docs on how roles map before you rely on it.
Next, the editions: which of these your plan actually unlocks.
## SSO feature comparison by edition
The decision gets made at the price gap between Pro and Business, because SSO sits in the paid tiers. The table shows what each edition costs and where it runs.
Read the "not published" cells as questions to put to n8n before you commit, not as gaps you can assume away.
| Edition | SAML | OIDC | LDAP | Price | Hosting | Limits | Audit |
|---|---|---|---|---|---|---|---|
| Community | not published | not published | not published | Free | Self-hosted | not published | not published |
| Cloud Starter | not published | not published | not published | 20 – 24 €/month | Cloud | not published | not published |
| Pro | not published | not published | not published | $50/month, billed annually | Cloud | not published | not published |
| Business | not published | not published | not published | 667 – 800 €/month | Cloud | not published | not published |
| Self-hosted Business | not published | not published | not published | not published | Self-hosted | not published | not published |
| Enterprise | not published | not published | not published | not published | not published | not published | not published |
Because the lower number is annual billing and the higher is monthly, each price is a range. Check protocol support and audit features against n8n's pricing page, docs and changelog before you buy.
Community is the free, self-hosted edition. It costs nothing, but you carry the upkeep, and n8n's pages are where to confirm what identity features it includes.
[ElseOps](https://elseops.com/blog/n8n-pricing/) puts Starter at 20 – 24 € per month, so a small team pays little to get started. Pro is $50 per month, billed annually, still a modest line item.
Business is 667 – 800 € per month, roughly thirteen times Pro, so if your identity provider needs a Business-level feature, you're budgeting for a different class of purchase.
n8n doesn't publish a separate price for self-hosted Business, so you can't compare it with the Cloud Business figure until you ask for a quote.
Enterprise pricing is also not published. Treat it as a sales conversation, and ask for protocol support and audit coverage in writing.
## Common mistakes when buying and enabling n8n SSO
When an n8n SSO rollout fails, it usually traces back to one of six assumptions, and each one can be checked against n8n's own docs before money moves or login gets enforced.
The set below pairs every mistake with its fix, so you can run a purchase or a setup plan against it.
- Assuming Community has SAML: check n8n's pricing and SSO docs for your edition first.
- Buying on execution counts: confirm SSO is in the plan, not just the volume.
- Leaving local password login open: restrict it once SSO works.
- Getting proxy or callback URLs wrong: set the public URLs n8n documents.
- Having no tested fallback admin: prove recovery before enforcing.
- Confusing licence with entitlement: the Sustainable Use License governs how you may use the code, while SSO access comes from a paid plan.
Four of these do the real damage, so they get detail below.
**Self-hosting the free Community edition doesn't hand you SAML or OIDC.** Those sit in paid tiers, so a team that plans around "free plus SSO" discovers the gap after the infrastructure is built.
Read the edition comparison on n8n's pricing page, then ask for the protocol you need in writing.
**If email-and-password login stays open beside SSO, anyone with an old credential skips your identity provider and its MFA.** Offboarding then looks complete while a local account still works. Check n8n's SSO docs for how to restrict it, and audit local users after go-live.
**Behind a reverse proxy, n8n builds redirect addresses from its configured URLs, not from what the browser sees.** If those point at an internal host, the identity provider rejects the callback or loops you back.
Set the editor and webhook URLs to your public address, and make the same address match in the provider.
**SSO misconfiguration locks out everyone at once, including you.** Keep one owner account with a stored credential, and test recovery, including n8n's documented CLI reset options, before you enforce SSO.
**SSO misconfiguration locks out everyone at once, including you.
Fix these six and the protocol setup itself is the short part of the job.
## Single sign-on in Activepieces for the same job
### Where Activepieces keeps SSO
Activepieces puts SSO in a Security page of its admin panel, with Google sign-in, SAML 2.0 and allowed email domains as separate switches. The edition question you just worked through still applies, but the protocol side is less to configure.
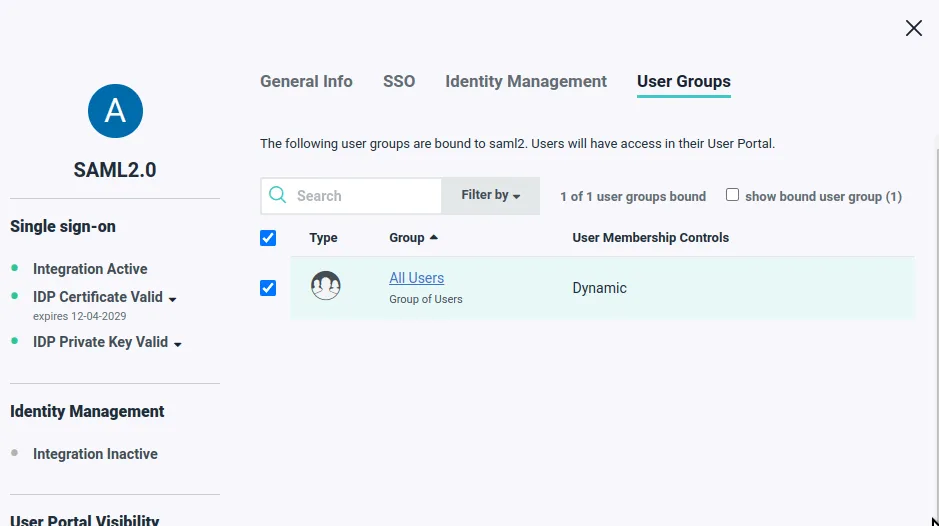
In the screenshot, Security is open in the left sidebar with "Single Sign On" selected, and the main panel lists four options: Allowed Domains, Google, SAML 2.0 and Allowed Email Login.

The first three each have an Enable button. Allowed Email Login is a toggle, and it's currently on.
Take two things from it. Google covers a team whose accounts already live in Google Workspace, so you don't need a SAML identity provider just to get single sign-on.
And the email toggle means password-style login stays open until you switch it off, so enabling SSO alone doesn't lock anyone out of the old route.
### Which edition unlocks it
The panel doesn't say which edition unlocks these settings, and I won't guess.
The pricing page lists Free at $0, Plus at $20 a month, Team at $200 a month and Ultimate through sales, so check Activepieces' SSO documentation against those four before you commit, using the same test as for n8n: your identity provider, your user count, your audit needs.
### n8n SSO licensing and free trial options
Licensing is simpler. The core is open source under the MIT licence, so you can self-host it without the usage restrictions that put some teams off n8n's Sustainable Use License.
The enterprise directories carry a separate commercial licence, while the core is MIT., including SCIM, custom RBAC, audit logs, release management and secret manager integration.
MoneyGram, Moneypenny, Alan and FundingSocieties run Activepieces in production.

There's also a free cloud plan that asks for no card, which lets you build a real workflow before anyone talks about budget.
Activepieces doesn't import or convert n8n workflows. You rebuild them, so check that the apps a workflow touches are among the 741 integrations in the open source monorepo, then try one small, annoying workflow first and judge the editor on that.
The free cloud plan at [activepieces.com](https://www.activepieces.com) is $0 with 1,000 credits a month, unlimited flows and up to 5 users, and when the credits run out, flows wait for the next day's credits.
Activepieces is the better fit for teams that need the full enterprise feature set (SSO, SCIM, custom RBAC, audit logs, release management and secret managers) under their own control, judged on whether an air-gapped install gives up anything compared with the managed cloud.
The docs list the same features either way, so choosing self-hosting costs no capability, and the SSO page shows a plain setup with Google, SAML 2.0 and allowed domains as separate switches.
A team that prefers a managed, region-pinned service with SOC 2 Type II may still reasonably go to the cloud, but it would be choosing that for operational convenience and not because it gets more features.
## The verdict on n8n editions
### Which n8n SSO plan to choose
Pick the The n8n edition that lists your identity provider, covers your user count and gives you the audit trail you need.
The exception is a free edition that already does all three, which is rare. Paying for SSO is the norm, not an n8n quirk.
What vendors charge for the SSO tier is tracked at [SSOPricing](https://ssopricing.com/). GitHub's uplift is 425%, so a team moving to SSO there pays more than five times the base price.
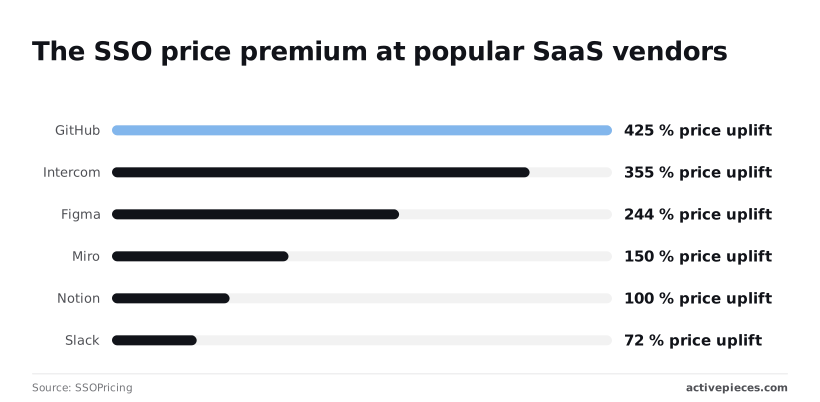
Intercom, the customer messaging tool, sits at 355%, and Figma, the design tool, at 244%, meaning customers pay 4.55× and 3.44× as much.
Miro, a whiteboard app, is at 150%, and Notion, a docs workspace, at 100%, which doubles the bill. Slack is lowest at 72%.
The lesson is that the gap between tiers is where the money goes, so budget for it before you plan the protocol work.
With a handful of users and no compliance reviewer, the verdict flips. Then shared logins with strong passwords may cost less than any paid tier.
1. Confirm your identity provider and protocol. Write down which one your company uses (Okta, Microsoft Entra ID, Google Workspace) and whether it speaks SAML or OIDC, so you can check n8n supports that exact pairing.
2. Re-check n8n's pricing page. Editions and limits change, so a figure from a blog post, this one included, is a lead and not a quote.
3. Request a trial or quote. Ask in writing whether SSO, your user count and audit logging are included in the edition you're pricing.
4. Test in staging with a fallback admin. Keep one local admin account outside SSO, or a misconfigured setting locks everyone out, you included.
5. Record the date checked. Put it next to the price in your decision note, so whoever renews next year knows how stale it is.
Once those five lines are in your notes, the actual protocol setup is an afternoon's work.
## Frequently asked questions
### Editions and sign-in methods
Does the n8n Community edition support SSO? No. SAML and LDAP sign-in sit behind n8n's paid editions, so the free self-hosted Community build gives you email-and-password accounts only. If your security team needs central login, that's the edition decision, not a setting you missed.
Can I use Google or Microsoft login with n8n without SAML? Not as a sign-in method on Community.
The Google and Microsoft credentials inside n8n connect your workflows to Gmail, Sheets or Outlook, and they don't log people into n8n. Sign-in through those providers goes through OIDC or SAML, which n8n gates by edition.
Check n8n's SSO docs for the protocols your edition lists.
### Provisioning, hosting and licences
Does n8n support SCIM user provisioning? I can't confirm SCIM from n8n's published pages, so don't plan around it.
Without it, someone removes leavers by hand, and that's how a departed contractor keeps access for months. Ask n8n sales in writing before you sign, and check the plan comparison page.
Is n8n SSO available on self-hosted plans? Yes, with a paid licence. Self-hosting doesn't exempt you from the edition gate: you run the servers, and you still buy a licence key that unlocks SSO.
So budget for the licence and for the upkeep of your own box, not one or the other.
What happens to SSO if my n8n licence lapses? Expect the licensed features to switch off, and that includes SSO.
Keep at least one owner account with a local password, so a lapsed renewal at month-end doesn't lock everyone out of workflows that run payroll exports or invoice reminders. Rehearse this on a staging copy, and read n8n's licence documentation for the exact behaviour.
## Related reading
- [GitLab Pricing in 2026: What Teams Pay](https://www.activepieces.com/blog/gitlab-pricing-in-2026-what-teams-pay)
- [Power Automate Pricing: Plans & Costs in 2026](https://www.activepieces.com/blog/power-automate-pricing-plans-costs-in-2026)
- [Zendesk Pricing Plans and Total Costs for 2026](https://www.activepieces.com/blog/zendesk-pricing-plans-and-total-costs-for-2026)
## References
- [SSOPricing](https://ssopricing.com/)
- [ElseOps](https://elseops.com/blog/n8n-pricing/)