Set an expiration that matches how long the job needs to run, so a forgotten token stops working by itself. Give the token a name that says what it's for; that name is what the approving user sees, and what you'll search for when you audit or revoke. Approve while signed in as the account the integration should act as, because the token inherits that user's board access. | | Identifies | Grants board access | Handling | |---|---|---|---| | API key | The application | No | Low sensitivity, but keep it out of public repositories | | Secret | The application, for OAuth signing | No | Treat as a credential and keep it in a vault | | Token | A user's approval of the application | Yes, within its scope | Highest risk; rotate and expire it | If several users must connect their own accounts, use an OAuth flow so each approves separately, rather than sharing one token. ## A minimal working Trello API request When one account is yours alone and nobody else needs to connect, the smallest working Trello integration is a GET to `/1/members/me/boards` followed by a POST to `/1/cards`, each carrying your key and token as query parameters. Because the query parameters are part of the URL, any proxy, access log or CI output that records the URL records your credentials with it. ### List your Trello boards with the API ```bash curl "https://api.trello.com/1/members/me/boards?fields=name,id&key=$TRELLO_KEY&token=$TRELLO_TOKEN" ``` You get a JSON array back, one object per board, holding the `id` and `name` you asked for. The `fields` parameter trims everything else, so you're not shipping data your code never reads.  If you get an empty array, the token works but can see no boards, which usually points to a scope or membership problem rather than a bad key. ```bash curl -X POST "https://api.trello.com/1/cards" \ -d idList=$LIST_ID \ -d name="First card from the API" \ -d key=$TRELLO_KEY \ -d token=$TRELLO_TOKEN ``` `idList` and `name` are the minimum. Trello returns the new card as a JSON object, including its `id` and a `shortUrl`. Sending the credentials in the POST body keeps them out of the request line, though they still sit in anything that records bodies. Don't paste a failing command into a ticket or chat without stripping them first. ### Find board and list IDs Take a board `id` from the first call and request `/1/boards/{id}/lists?fields=name,id`. The result's every list on that board with its ID, and the one you want goes into `idList`. Store these IDs in configuration. Looking them up on every run wastes a call, and a renamed list won't break a stored ID. ## Trello API endpoints, rate limits and plan tiers Every one of those lookups counts against a quota. [Trello's docs](https://developer.atlassian.com/cloud/trello/guides/rest-api/rate-limits/) allow **300 requests per 10 seconds per API key** and 100 per token. 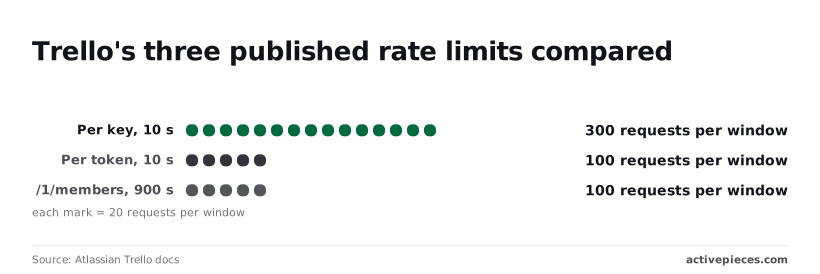 Spending won't get you past these rates: the **plan you pay for doesn't raise either number**, so your applications can't exceed them. As of November 2026, the API groups into seven resources. | Resource group | Purpose | Key operations | |---|---|---| | Boards | Top-level workspace container | Get, create, update | | Lists | Columns on a board | Get, create, archive, move | | Cards | Units of work | Get, create, update, move | | Checklists | Sub-tasks inside a card | Get, create, add items | | Members | People and their access | Get member, list boards | | Webhooks | Push notifications on changes | Create, list, delete | | Search | Cross-board queries | Query cards and boards | Of the seven, **only webhooks let you stop polling** the other six. ### Published rate limits Look at the three published windows side by side in the chart below. Per [Developer](https://developer.atlassian.com/cloud/trello/guides/rest-api/rate-limits/) guidelines, the key limit is three times the token limit, and the members limit is the tightest because its window is 900 seconds, not 10. Three tokens each running at their full 100 requests per 10 seconds would exhaust one key's 300 and start drawing HTTP 429 responses, which means requests are rejected. According to Atlassian Trello docs, the key limit is shared across them.  One call every nine seconds is roughly all you get on `/1/members`: per Atlassian Trello docs, the limit is **100 requests per 900 seconds**, meaning changes to member status won't be detected for at least nine seconds. A loop that fetches member data per card will hit the ceiling almost at once. Retrying immediately makes it worse, so back off and cache member lookups. Upgrading the plan doesn't change API access. [Trello's pricing page](https://trello.com/pricing) lists Free at $0 per user per month, Standard at $5, Premium at $10 and Enterprise at $17.50. 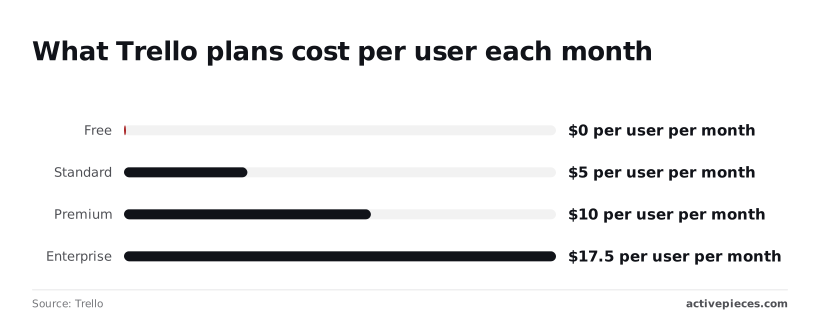 The rate-limit documentation lists no per-plan figures, so moving from $0 to $17.50 buys features, not request headroom. **Budget for batching and webhooks, not an upgrade.** ## Trello API errors you will hit in production If a call fails and nobody can tell why, you lose the same engineering time that batching and webhooks cost. It pays to know the handful of errors Trello returns before they reach a log. Read the 404 row of the table below first, because it's the one most often misdiagnosed as a bug in your code. The table pairs each symptom with its cause and fix. | Symptom | Cause | Fix | |---|---|---| | 400 Bad Request | Malformed board, list or card id, or a missing required parameter | Validate ids before the call; log the full request URL with the key and token stripped | | 401 Unauthorized | Token revoked, expired, or issued for a different key | Re-authorize, store the token in a vault, and rotate on a schedule | | 404 Not Found | The resource exists but's a private board the token's member can't see | Check membership of the authorizing user, not the URL | | 429 Too Many Requests | Burst traffic or polling exceeded the rate limit | Back off on the response, replace polling with webhooks, batch reads | | Oversized response | Unfiltered request returns every field, action and attachment | Request only needed fields and cap nested collections | Most of these are cheap to fix once the cause is named; the rest of this section covers the ones that need more than a one-line change. ### 401 and expired tokens Usually at night, a 401 arrives: the token that was valid for months has been revoked or was set to expire. Nothing in your code changed, so the failure looks random. Treat the token as a credential with a lifetime: keep it in a vault, record when it was issued and which scopes it carries, and alert on the first 401 rather than retrying it. When the board is private and the token can't see it, **Trello returns 404, which hides its existence**. The board is there; the authorizing member isn't on it. Before debugging the id, confirm that member's access. A token from a personal account fails on team boards for exactly this reason. Send requests faster than the API allows and you get a 429. Honor the response, back off, and stop polling: a webhook delivers the change, and a batch call collapses many reads into one request. If you request a board with no field filter, you get actions, members and attachments you never use, and the cost is slow calls and memory pressure in the worker. Ask for named fields only, and page the collections that grow without bound. ## Replace Trello API polling with webhooks and backoff Fields and paging shrink each request, but webhooks remove the requests that never needed to happen: register one per board and let Trello call you. Most of the time, a poller spends rate limit asking "anything new?" and hears "no". The table shows what each approach costs on the three dimensions that matter; the takeaway is that only polling pays for silence. | Approach | Latency | Rate-limit use | When the receiver is down | |---|---|---|---| | Polling | Up to one interval | Every request counts, changed or not | Nothing's lost; the next poll catches up | | Webhooks | Seconds | Near zero after registration | Trello retries, then gives up | | Workflow tool | Seconds | Near zero | The tool's the receiver, so your own outage doesn't drop events | Reply 200 immediately, queue the work, and process it afterwards: that's the duty webhooks bring. Trello signs each callback, so recompute the HMAC over the body plus your callback URL and compare it with the header before trusting anything. An unverified endpoint accepts a forged "card deleted" from anyone who finds the URL. ### Trello webhook retry schedule and receiver downtime Per the [Atlassian Trello docs](https://developer.atlassian.com/cloud/trello/guides/rest-api/webhooks), [Trello](https://trello.com/pricing) waits 30 seconds after the first failed delivery and 60 seconds after the second, so your app won't learn about failures immediately.  It makes its final try 120 seconds after that, by which point the system has been retrying for over three minutes, so endpoints still offline at that point will never receive this event. If a deploy takes your receiver down for more than a few minutes, events are lost, and repeated failures can disable the webhook. Keep the receiver thin and run a reconciliation fetch after any outage. When Trello returns 429, wait and retry with growing delays and jitter instead of hammering. Cache board and list lookups that rarely change. Request only the fields you use, so a reconciliation fetch stays cheap and doesn't eat the budget the webhooks just saved. ## Use the Trello integration in Activepieces Activepieces has a Trello integration among its 750 integrations, in which a card event can act as the trigger that starts a flow, and a flow can create a card, so you can automate workflows initiated by Trello activity.  That covers both directions of the plumbing this article has been working through: reacting to a card moving, and writing a card from somewhere else, without you hand-building either side against the raw API. The failure it addresses is specific. A webhook callback URL goes down or changes, Trello stops delivering, and nobody notices until a card is missing downstream. The Trello key and token live in a stored connection that the flow references, so they don't sit in your repository, your deploy config or a chat thread. MoneyGram, Moneypenny, Alan and FundingSocieties run Activepieces in production.  ### When a workflow tool is enough Start with the Activepieces Trello integration page, which lists the triggers and actions available, including the card events that can start a flow and the operations a flow can perform on a board. Trello is one of the 750 integrations counted in the open source monorepo, whose core is MIT-licensed, so the integration's triggers and actions are readable in source as well as on the page. If the thing you need is there, you're describing a process, not building plumbing. Describe the card-move process in the built-in chat and what comes back is a published flow in your account, whose Trello trigger and actions match that integration page and whose run trace lists every step of every run. What follows is the test for fit. A flow that reacts to a card moving, posts to another app and records the result is a good fit. So is a form that opens a card with the right fields filled in. ### When to call the API directly Write direct code when the flow needs something the integration doesn't expose. That includes an endpoint absent from the integration page, a bulk operation over a whole board, or request-level control such as the field selection from the previous section. Use code too when the logic's a program in its own right, with branching, state and tests that belong in your repository's review process. In those cases keep the scoped token and the managed webhook, and write only the part the tool can't. ## Frequently asked questions Where the advice above meets Trello's own rules, the answers are short. Is the Trello API free to use? Yes, Trello doesn't charge for API calls. The cost shows up elsewhere: rate limits still apply, so a polling loop that's free to write can still get throttled, and the throttling lands on whoever is running it. Do I need a paid Trello plan to use the API? No, a key and token work against boards on a free workspace. Plan tier affects what the workspace offers, such as board features and automation allowances, not whether the API answers. Check Trello's current documentation for limits before sizing a design around them. Can one API key serve many users? Yes. The key identifies your application, and each user authorizes it separately and receives their own token. Keep it that way: one shared token across users means one leak exposes every board it can reach, and you can't revoke access for one person without cutting off everyone. ### How do I make a Trello token that never expires? Request it by setting the expiration parameter to never in the authorization URL. Treat that as a decision with a cost. Until someone revokes it from the account's settings, a token that never expires stays valid, so pair it with the narrowest scope that works and a recorded owner. An expiring token is the better default for anything that doesn't run unattended. Does Trello have an official API client library? I know of no client library that Trello itself maintains for general use. The documented REST endpoints are the supported surface, and community wrappers fill the gap. Before adopting one, read what scopes it requests and when it last changed, since a wrapper that asks for more access than you need is the over-scoped token problem in another form. ## Related reading - [Replacing Airtable API Keys with Personal Access Tokens](https://www.activepieces.com/blog/replacing-airtable-api-keys-with-personal-access-tokens) - [How to handle errors in production AI agents](https://www.activepieces.com/blog/how-to-handle-errors-in-production-ai-agents) - [How to Build an AI Agent Harness for Production](https://www.activepieces.com/blog/how-to-build-an-ai-agent-harness-for-production) ## References - [Atlassian Trello docs](https://developer.atlassian.com/cloud/trello/guides/rest-api/webhooks) - [Trello](https://trello.com/pricing) - [Atlassian Trello docs](https://developer.atlassian.com/cloud/trello/guides/rest-api/rate-limits/)By the time anyone clicks approve, the risk has already been decided in the authorize URL.