Workato SSO Explained and How to Set It Up in 2026

Oct 27, 202614 min read
What Workato SSO is and covers
What Workato SSO is, in short
Workato SSO is SAML-based login to the Workato platform through your company identity provider. It governs how your people sign in to Workato, not how recipes authenticate to other apps, much as it would in any automation tool such as Activepieces.
I haven't confirmed a plan name or price for SSO, so I state none. Workato's docs are the source for plan eligibility, pricing and limits.
Ask Workato, or read the current docs page, before you commit. Terms change, and a stale claim here would cost you.
Identity providers and protocols Workato documents
"We support SSO" means nothing until a protocol name is attached, and for Workato's user login that name's SAML.
Use the list in Workato's docs as your authority, because it documents setup for specific identity providers. If your provider isn't listed, check whether it can issue a standard SAML assertion before you assume it'll work.
"We support SSO" means nothing until a protocol name is attached, and for Workato's user login that name's SAML.
Settle these before you touch the enforcement setting:
- Confirm the plan that includes SSO, in writing, from Workato.
- Collect the SAML values your identity provider issues: the sign-in URL, the issuer and the signing certificate.
- Match them to the fields Workato asks for in its SSO settings.
- Create a break-glass admin who can still sign in if SAML fails.
Skip step 4 and a bad certificate or a mistyped URL locks every user out, you included.
Logging in to Workato versus connecting apps
SSO covers only one of two separate authentication paths. The illustration below shows an employee signing in to Workato through the identity provider over SAML on one side.
On the other side, a recipe connects to an external app with its own API key or OAuth. A divider labels the two. Take from it that turning on SSO changes the left path and leaves the right one alone.
That split has a practical consequence. Enforcing SSO doesn't rotate, replace or protect the API keys and OAuth grants your recipes use. Those credentials live in each connection and need their own review.
Locking down a network is where SSO usually goes missing, because the self-hosted or air-gapped build is often the stripped one.
Activepieces doesn't do that: the access control you configure for SSO, along with SCIM provisioning, custom roles, audit logs and secret managers, runs in the air-gapped edition just as it does in the managed cloud, so closing the network doesn't cost you the control you settled on.
MoneyGram, Moneypenny, Alan and FundingSocieties run it in production.
This takes minutes, not a project: automate it in Activepieces free.
Plan, licence and price requirements for Workato SSO
Before anything else, settle the plan. **Workato's pricing page lists SAML SSO and MFA under the Standard edition but publishes no price for it, so get the cost from sales in writing before you plan anything else.
What Workato publishes and what it leaves to sales
You will find no per-seat or per-tier price on Workato's pricing page, and no SSO line item either. Its documentation describes SAML-based single sign-on, but the docs are the place to confirm the protocol and the setup fields.
Neither the docs nor the pricing page tells you what the feature costs.
Treat "Workato supports SSO" as incomplete until sales names the plan, the contract term and any limits, such as which user types or workspaces are covered.
Ask for four things:
- The exact plan or add-on that enables SSO.
- The price, quoted as an uplift over your current contract.
- Whether SSO covers every workspace and user role.
- Whether the quote holds at renewal.
Because SSO's often priced as a jump, not a small add-on, the last question matters. SSO Pricing tracked the extra cost of reaching the SSO tier on popular SaaS products:
- HubSpot rises 2043 %, so the feature can cost many times what the base product does.
- GitHub rises 425 %, which is more than a fivefold bill for the same seats.
- Intercom rises 355 %, so a small team can be priced out of SSO entirely.
- Zoho CRM rises 271 %, meaning even a mid-priced tool can nearly quadruple.
- Figma rises 244 %, so the jump is normal for design tools, not a quirk of CRMs. Notion rises 100 %, still a doubled bill, which means you can't choose an option that doesn't significantly increase costs.

A quote with no uplift is the surprise, not a quote with a large one. None of these figures is a Workato price; they show the range.
Clarifying SSO requirement gaps
Read Workato's published position as a list of gaps to close with sales, not as a statement that the feature is free.
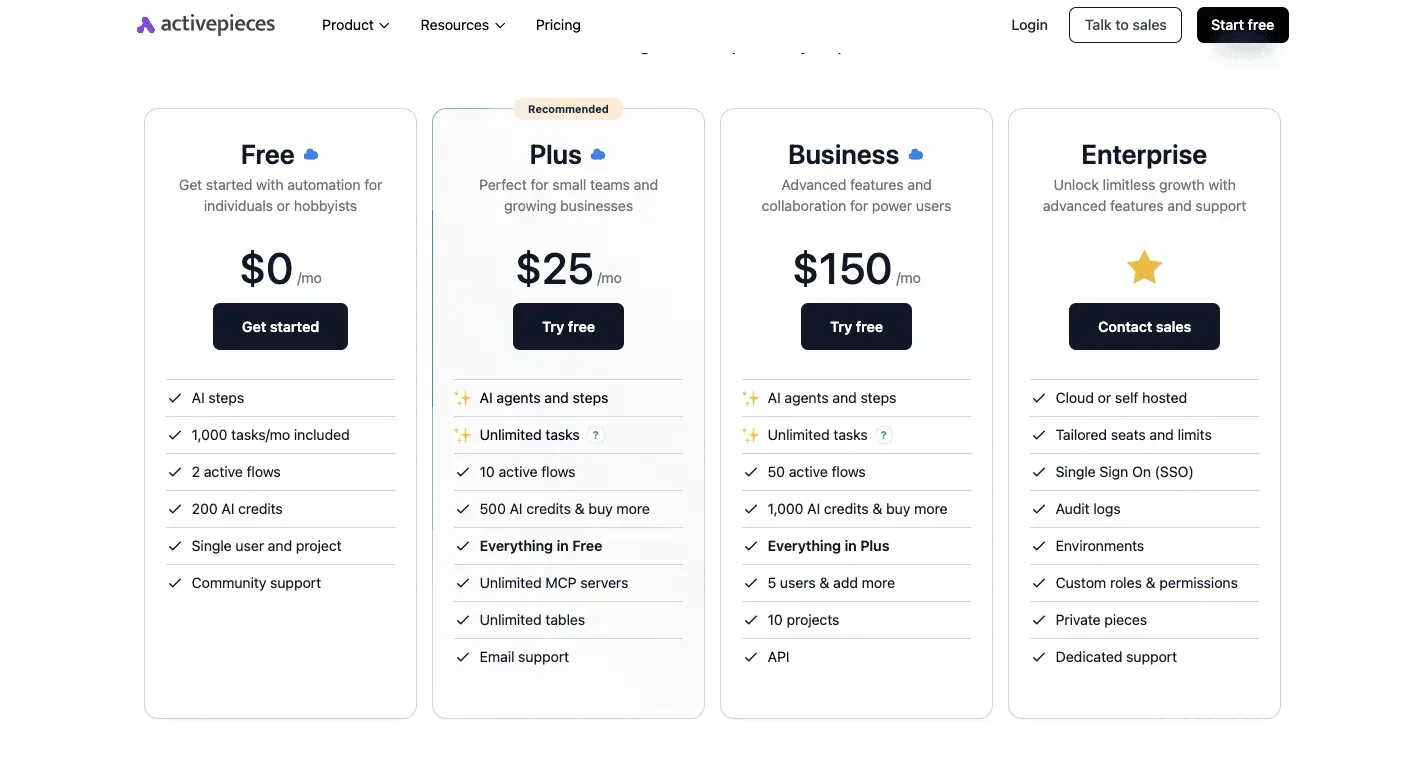
Workato names no plan for SSO and publishes no price, and it's a cloud product (https://www.workato.com/pricing). Activepieces lists the Enterprise plan for SSO, runs on cloud or self-hosted, and quotes a custom price (https://www.activepieces.com/pricing).
Workato SSO setup with SAML
Four stages, one sitting: first copy Workato's service provider values, then build a SAML app in your identity provider (IdP), paste the IdP's details back into Workato, and test one user before enforcing anything. Leave a second admin session open the whole time.
Stage 1: Collect Workato's service provider values
Open the SSO settings in your Workato workspace and find the SAML section. Copy two values: the ACS URL (where the IdP posts its sign-in assertion) and the entity ID (Workato's identifier in the exchange). Paste both into a scratch file.
If a first sign-in fails, a typo in either value is the usual reason. Field labels change between releases, so check them against Workato's current docs.
In Stage 2 you build the SAML app in your identity provider. Create a new SAML 2.0 application, then:
- Put the ACS URL in the single sign-on (assertion consumer) URL field.
- Put the entity ID in the audience field.
- Set the name ID to the user's email address.
- Map three attributes: email, first name and last name.
- Assign one test user, not the whole company.
Get the email mapping right above all. Sign-in matches people by email, so the address the IdP sends must match the address on the Workato account exactly.
Stage 3: Enter the IdP details in Workato
From the IdP you need three things:
- A sign-in URL
- An issuer
- An X.509 signing certificate
Paste each into its matching field in Workato. Paste the certificate whole, including the begin and end lines, because a clipped certificate fails signature checks. Save the settings, but leave enforcement off.
To see the choice you're making here, look at another automation platform's admin console. Its SSO page lists domain-based sign-in, Google, and SAML 2.0 as separate options, plus a toggle that keeps plain email login switched on.

You want SAML 2.0, and you want any equivalent email-login fallback left on until the test passes.
That toggle is the safety net, and Stage 4 is the test with one user before enforcing. While the toggle stays on, a mistake in Stages 1 to 3 costs you a retry, not a lockout.
- Open a private browser window.
- Start sign-in through SSO as the assigned test user.
- Confirm you land in the right workspace with the correct name and email.
- Keep your original admin session open the whole time.
Only when that works should you consider enforcing.
You can follow the rest of this with the builder open. Start free, no card.
Common Workato SSO mistakes to avoid
Five mistakes cause most Workato SSO lockouts: enforcing before testing, NameID or email mismatches, expired certificates, offboarding gaps, and assuming SSO covers API clients. The break-glass admin protects you from the first one, and the fixes below cover the rest.
Avoiding admin lockout when enforcing Workato SSO
Test with one non-admin account before you enforce SSO. Then test with an admin account in a private browser window while your original session stays open. Enforce only after both sign-ins succeed.
If you enforce first and the IdP configuration is wrong, nobody can sign in, and the break-glass account is your only way back. Check Workato's docs for how enforcement behaves on your plan.
Workato SSO NameID and email mismatches
Send the wrong NameID and nothing matches: it must equal the user identifier Workato expects, usually the email address. Check the exact format in Workato's docs.
Send j.smith@ where Workato holds john.smith@, or differ only by case, and you get a failed login or a duplicate user.
Fix it by sending the email attribute exactly as stored in Workato, and compare a test assertion against a real user record before rollout. This is general SAML practice, not a Workato-specific rule.
Workato SSO SAML certificate expiry
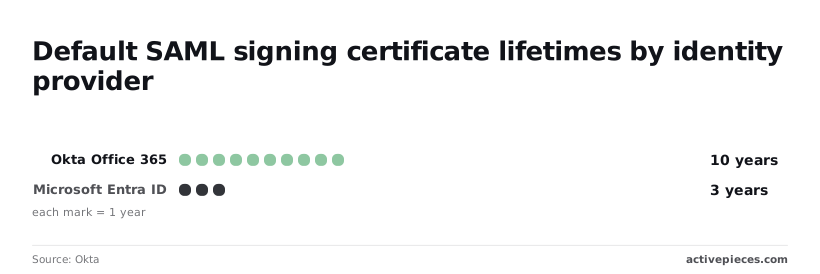
When the SAML signing certificate lapses, every SSO login fails at once. Defaults differ by IdP.
10 years is the default that Okta's certificate rotation guide gives for an Okta Office 365 app. That's long enough for the person who set it up to have left, so the expiry needs a calendar entry or it'll be forgotten.
On the same page, Microsoft Entra ID is listed at 3 years, so a renewal will arrive within a normal staffing cycle.
Put the expiry date in a shared calendar with reminders at 60 and 30 days, so you're prompted to act well before the deadline. Upload the new certificate to Workato before the old one lapses. This is general SAML practice.
Offboarding users and role gaps in Workato SSO
Disable the IdP account and Workato must honor that, or the person keeps their access.
Two gaps remain, both worth confirming in Workato's docs: existing sessions may stay active until they expire, and Workato-side accounts and roles may need removing by hand if you don't use automated provisioning.
Add "remove from Workato" to your offboarding checklist, then verify it by trying a disabled test user.
The bigger gap is API clients. SSO governs interactive logins. API tokens and client credentials are separate, so a departing employee's tokens can keep working. Rotate or revoke them as part of the same checklist.

Where Activepieces fits if SSO is your real requirement
If SSO is the requirement, Activepieces sells it on its Team plan. Its 2026 cloud pricing guide lists that plan at $200 a month, up from $150. The entry plan doesn't carry it, so budget for Team from the start.
When to compare Workato SSO with other platforms
If you're choosing between platforms and SSO is a hard requirement, this matters. If Workato is already signed and working, stay with it and finish the lockout-proofing above.
What to take from it is that the entry tier got cheaper while the SSO tier got dearer.
(chart: Activepieces cloud prices before and after the 2026 change)

Plus fell from $25 to $20 a month. That's cheaper, but it's not the plan with SSO, so it doesn't solve your problem.
For each workspace you put on Team, the SSO plan, the rise from $150 to $200 a month is a $50 monthly increase, or $600 a year, and so your costs compound with each workspace added.
Price it at $200, not at the figure in an older comparison article, meaning that article's data is now out of date.
The pricing guide covers cloud plans. I haven't confirmed a figure for SSO on a self-hosted install, so don't assume one.
Ask Activepieces in writing which plan or licence unlocks SSO for self-hosting, and which protocol it uses (SAML or OIDC). Do the same with Workato: read its own documentation for the plan and protocol before you compare anything.
What to do on Monday: do these in order, and don't skip ahead to enforcement.
- Confirm the plan in writing. Get an email or order form from your vendor that names SSO as included in your plan. A sales call doesn't count. Keep it with your contract records.
- Create a break-glass admin outside SSO. Make a local admin account with a long, unique password and no SSO link. Store the password in your vault, not in someone's head. Confirm that the account can still sign in when SSO enforcement is on, because some platforms exempt local admins only if you set it explicitly.
- Test one user. Pick a non-admin and sign in through the identity provider. Check that the account lands in the right role. Only then enforce SSO for everyone.
- Set a certificate expiry reminder. Open the signing certificate in your identity provider, read its expiry date, and put a calendar reminder 30 days before it, giving you a month to arrange renewal. An expired certificate stops every SSO login at once, and the break-glass account from step 2 is how you get back in.
Frequently asked questions
Confirm each of these in Workato's own documentation, which was last checked for this article on 27 October 2026; the steps above leave them open.
Does Workato support Okta and Microsoft Entra ID for SSO?
Because Workato's SSO is built on SAML 2.0, any identity provider that issues SAML assertions can work in principle. Okta and Microsoft Entra ID both do.
Look for a Workato setup guide naming your provider. If one exists, follow its attribute and name ID settings exactly. If none exists, treat your setup as a generic SAML configuration and test it with a non-admin account first.
Can I still log in with a password after enabling Workato SSO?
It depends on the enforcement setting, and the docs are the authority. Find the exact wording on whether password login is blocked for all users, or whether admins can still use it. Don't assume admins are exempt.
Check API clients too. Integrations that call Workato's API usually authenticate with tokens, not a browser login. Confirm that enforcing SSO doesn't break them, and test one before you enforce.
Does Workato support SCIM user provisioning?
Don't assume it does because SSO works. SSO controls who can sign in. SCIM controls who gets created, changed and removed. Search Workato's docs for SCIM by name and check which identity providers are listed.
If it isn't supported for your plan, deprovisioning stays manual. A person removed from your identity provider may then keep a Workato account until an admin deletes it.
Is Workato SSO included in every plan?
Nothing in the public docs that we verified lets us say yes. SSO is often tied to a higher tier or a contract term. Ask your Workato account contact in writing which plan includes SSO, whether enforcement is a separate entitlement, and what it costs.
Get the answer before you design the rollout. Otherwise you may build a plan around a feature your contract doesn't cover.
If login breaks, start the rollback with the break-glass admin account you set up before enforcing. Follow these steps:
- Sign in with that account, using whatever method the docs say it can still use.
- Turn off SSO enforcement in the workspace security settings.
- Fix the identity provider settings, such as the certificate, the ACS URL or the attribute mapping.
- Test with a non-admin user, then enforce again.
If the break-glass account also fails, contact Workato support. Find their lockout procedure in the docs now, not during an outage.
Related reading
References
Build it
Set this up in minutes.
No code required. Connect your accounts, and Activepieces runs it from there.
Start free Talk to sales