Is Zapier GDPR Compliant? What to Check Before Buying
Oct 18, 202614 min read
You can use Zapier in a GDPR-compliant way.
It does so through a signed contract and your own configuration: it acts as your processor, and compliance is something you assemble, not a setting you enable, much as it would be with any automation tool, whether that's Zapier or an open-source option like Activepieces.
Zapier GDPR compliance is the arrangement under which Zapier, as your data processor, supplies published security controls and a data processing agreement, while you, as controller, remain responsible for the lawful basis, the signed DPA and the personal data each of your workflows carries.
As of 18 October 2026, its published position sits on its trust page, and the plan you need for any extra controls is on its pricing page.
Zapier GDPR compliance, answered with the date checked
What GDPR compliance means for an automation tool
When a team builds a workflow that copies customer email addresses and support notes from a form into a spreadsheet, then into a team chat channel the whole company can read, a vendor breach is not what goes wrong.

Every vendor involved can be certified and the workflow is still unlawful, because nobody decided it should carry that data.
Your workflow data sits in three places:
- the trigger app
- Zapier's own task history
- the destination app
Zapier's subprocessors can touch the middle one.
Zapier GDPR controller and processor roles
Under GDPR, you decide why and how personal data is used, which makes you the controller. Zapier handles that data on your instructions, which makes it a processor. The split below follows from that.
- Zapier, as processor, publishes the data processing agreement, its security controls and its list of subprocessors.
- You, as controller, own the lawful basis for each use of personal data and the decision to accept the DPA.
- You also own data minimisation, meaning what each workflow is allowed to carry.
- The content of every workflow, including which apps receive the data, is yours.
Nothing in the vendor's column can fix a gap in yours, and the DPA does nothing until someone on your side accepts it and records that they did.
Date checked and where each claim comes from
Because trust pages change without notice, every vendor claim in this article is tied to a page Zapier publishes, and each will be marked with the page it came from.
Apply the same discipline to any alternative. Activepieces has an MIT-licensed core you can self-host, which shrinks the contract question, but the lawful-basis question stays yours.
Everything below works on Activepieces' free plan. Start without code or a credit card.
Zapier compliance features by plan
Which plan unlocks each control is something you must read off Zapier's trust and pricing pages, not assume, even though it publishes a data processing agreement, security attestations and single sign-on.
Against each requirement, the table below sets what Zapier states, the plan it attaches to and the cost. Where a page is silent or ambiguous, the last column says so, and you should treat that cell as unconfirmed until Zapier answers in writing.
| Requirement | What Zapier offers | Which plan | Cost | Flag |
|---|---|---|---|---|
| DPA | A published data processing agreement | Not stated as plan-gated | No separate charge stated | Confirm it covers your account type and lists current sub-processors |
| SOC 2 report | Attestation referenced on the trust page | Unclear | Not stated | Check whether you get the full report or a summary, and under NDA or not |
| SAML SSO | Single sign-on for team accounts | Higher tiers; confirm which | Included in the plan price, per the pricing page | Page wording on the exact tier is unclear |
| Data retention controls | Task history and data-handling settings | Varies by plan | Not stated | Retention periods and deletion options need confirming per plan |
| Plan price | Tiered pricing, with an enterprise tier on request | All plans | Set on the pricing page; enterprise by quote | Task volume changes the bill, so price your real workflows |
| ISO 27001 | Not confirmed on the pages reviewed | Unknown | Unknown | Don't assume; ask for the certificate |
The cost of meeting your requirement isn't visible until you talk to sales, because the enterprise tier is quoted, not listed. SSO and the more granular data controls are what tend to sit on upper tiers.
What to verify before relying on the table
Work through these in order:
- Open the DPA and read the sub-processor list and transfer mechanism yourself.
- Ask for the SOC 2 report itself, with its period and scope, not the badge.
- Get the plan for each control confirmed in an email you can file.
Do not read the DPA as more than it is: it covers Zapier's processing. It doesn't decide your lawful basis or what personal data each workflow carries, and those remain yours.
Zapier data location and subprocessors
Start at the trigger app, the first hop. The second is Zapier's task box with its stored history and a ring of hosting, monitoring, support and AI vendors around it. The three subsections below take the middle hop in turn.
Zapier task history and data retention
After the destination app has received a customer's email, address or support message, a copy of it is still inside Zapier. Task history is the failure mode to plan for.
That copy is in scope for erasure, even if you delete the record in your CRM.
Read what your plan holds before assuming retention is short, since it is a setting and a plan feature on Zapier's own pages.
Zapier subprocessors and non-EU data transfers
In Oct 2022, Zapier's subprocessor page listed 11 subprocessors, so a DPA signed then covered a short, reviewable list. The list reached 13 in Nov 2023 and 15 in Aug 2024, two additions per revision, which is small enough to skim.

By Oct 2026 the list stood at 37, so 22 vendors arrived after Aug 2024. That's more than triple the 2022 list, and the Oct 2026 count is the one your transfer assessment has to cover.
Check whether any workflow sends content to the AI vendors on the list. I found no EU-region option for task data documented on that page.
Treat that as a transfer outside the EU until Zapier states otherwise in writing, and put it in your transfer impact assessment.
Erasure and access requests
When a data subject asks you to erase their data, you must remove it from every place your workflows copied it. That means the trigger app, the destination app and Zapier's task history, and the subprocessors holding any part of it.
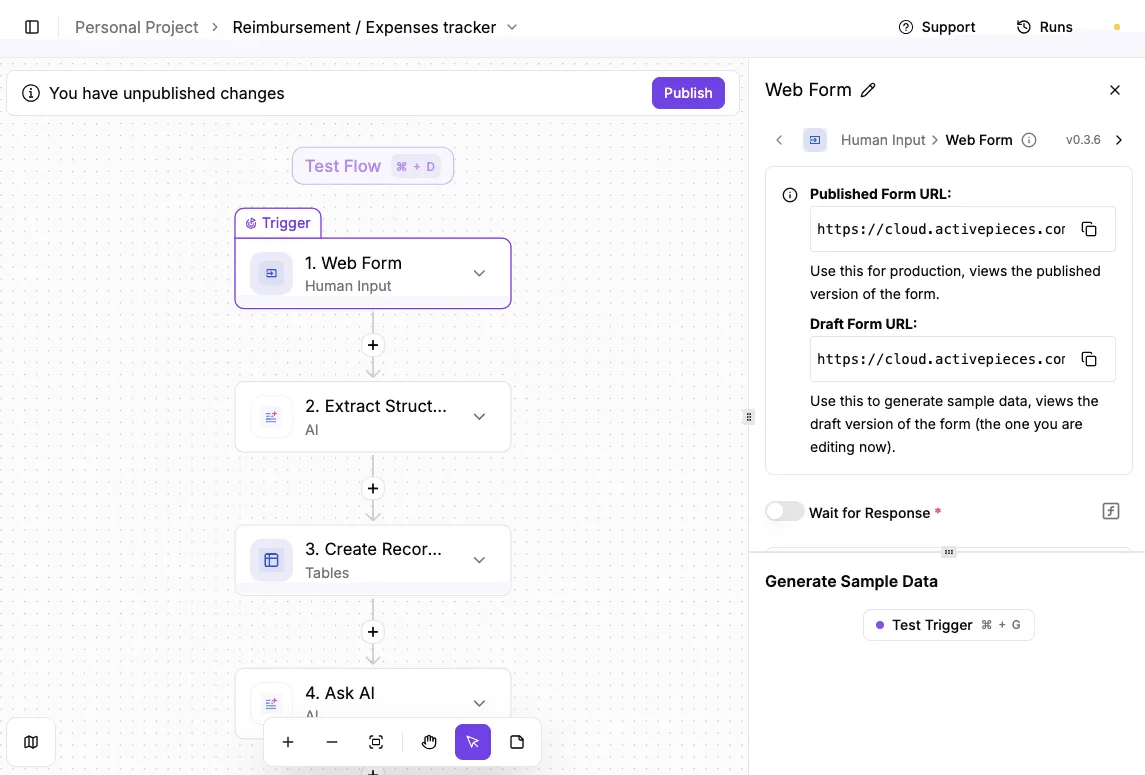
You must run the request and keep a record that each copy was deleted, though Zapier publishes the controls. Before go-live, ask Zapier how task-history deletion works and how long it takes, and get the answer in writing.
Easier to see it running than to read about it: set it up free, no card.
Five GDPR mistakes teams make with Zapier workflows
Whatever Zapier certifies, five mistakes cause most of the exposure. They are running workflows on personal accounts, sending more personal data than needed, leaving task history on, ignoring what connected apps do with the data, and never signing the data processing agreement (DPA).
When an employee builds a workflow on a personal login and then leaves, the workflow keeps running, moving customer records under an account your company can't audit, reassign or close.
You can't answer an access request about data that flows through a login you don't control. Put every production workflow under a company-owned account with named owners.
Over-sending personal data
Forward a whole form submission to five apps when two need only an email address, and every later obligation widens. Each extra field is data you must justify, secure and delete.
Worse, task history records what each step received, and retention runs 29 to 69 days depending on plan.
So a field you over-sent can sit in Zapier for up to about two months after the workflow handled it, and a deletion request has to reach that copy too.
Send only the fields each step needs, and switch history off for workflows that carry personal data.
GDPR risks from apps connected to Zapier
In a chain of processors, Zapier is only one. If a workflow writes a lead into a CRM, a support desk and a spreadsheet, each of those apps receives the data under its own terms and may store it outside the EU.
None of that transfer is covered by Zapier's controls. List every app a workflow touches, find where each processes data, and confirm a transfer mechanism exists for each.
Without a signed DPA you have no written record of what Zapier may do with the data, which Article 28 requires. Download it, sign it, and store it with the list of workflows it covers. An auditor will ask for this document before anything else.

Where regulators actually look
974 enforcement actions under Article 5 (lawfulness) and 690 under Article 6 (legal basis), against 274 under Article 32.1 (security), are recorded by the CookieFines tracker. Together, lawfulness and basis draw about six times as many actions as security.

What gets fined is decisions you make about what to collect and why, not a vendor's missing certificate.
When Activepieces fits a stricter residency requirement
When your requirement is that workflow data stay in a region or a network you choose, Activepieces fits.
What gets fined is decisions you make about what to collect and why, not a vendor's missing certificate.
It has a managed cloud in an EU or US region with SOC 2 Type II, and a self-hosted option, air-gapped if you need it, that never sends data outside your environment. MoneyGram, Moneypenny, Alan and FundingSocieties run it in production.
That ranking of residency demands sets the order of the vendor questions below, and the table shows where the two products differ on the controls those questions touch.
Read the Zapier column as what Zapier documents on its own pages, and verify each cell there before relying on it.
| Requirement | Zapier as documented | Activepieces |
|---|---|---|
| SOC 2 Type II | Check Zapier's trust pages for the current report and scope | Offered |
| SSO/SCIM | Check Zapier's plan pages for the tier that includes it | SSO and SCIM offered |
| Custom RBAC | Check Zapier's documentation for role granularity | Custom RBAC offered |
| Audit logs | Check Zapier's plan pages for availability and retention | Audit logs offered |
| Hosting (EU/US cloud, self-host, air-gap) | Check Zapier's documentation for hosting and region options | Managed cloud in an EU or US region; self-host; air-gap |
The air-gapped self-hosted build is not a cut-down edition: the same six enterprise controls (SSO, SCIM, custom RBAC, audit logs, release management and secret managers) appear in its docs as in the managed cloud's, whether that cloud is pinned to the EU or the US.
Tighter residency therefore does not cost you a control. A listed control is still a claim, so the security documents, not this table, are what you attach to your record.
Managed cloud in an EU or US region
Activepieces' managed cloud lets you choose an EU or US region up front, and it carries SOC 2 Type II, which prevents a workflow payload landing in a region your DPA never named.
The answer to "where is this processed" is then a deployment decision you can write into the contract rather than a default you discover later.
Confirm the region applies to workflow data and run logs, not only to the account record.
Self-host and air-gap
Run Activepieces, whose core is MIT-licensed, on infrastructure you control and the boundary moves from a contract clause to a network edge. An air-gapped deployment keeps data from leaving your network at all.
If you are a regulated team, you can use this to keep data in your own environment. That's an architecture, not a certification: it doesn't give you a HIPAA attestation or an ISO certificate, and nothing here claims either.
You also take on patching, backups and uptime, which the managed cloud would otherwise carry.
Access control and audit logs
Residency says where data sits; access control says who can touch it. Activepieces provides SSO and SCIM in both the managed cloud and the air-gapped build, so joiners and leavers follow your identity provider instead of manual cleanup.
Custom RBAC lets you restrict who can edit a workflow that handles personal data, and audit logs give you the record of who changed what when a regulator or customer asks.
Before you sign, ask each vendor which plan includes each control, what the audit logs record and for how long, and which regions apply to run data.
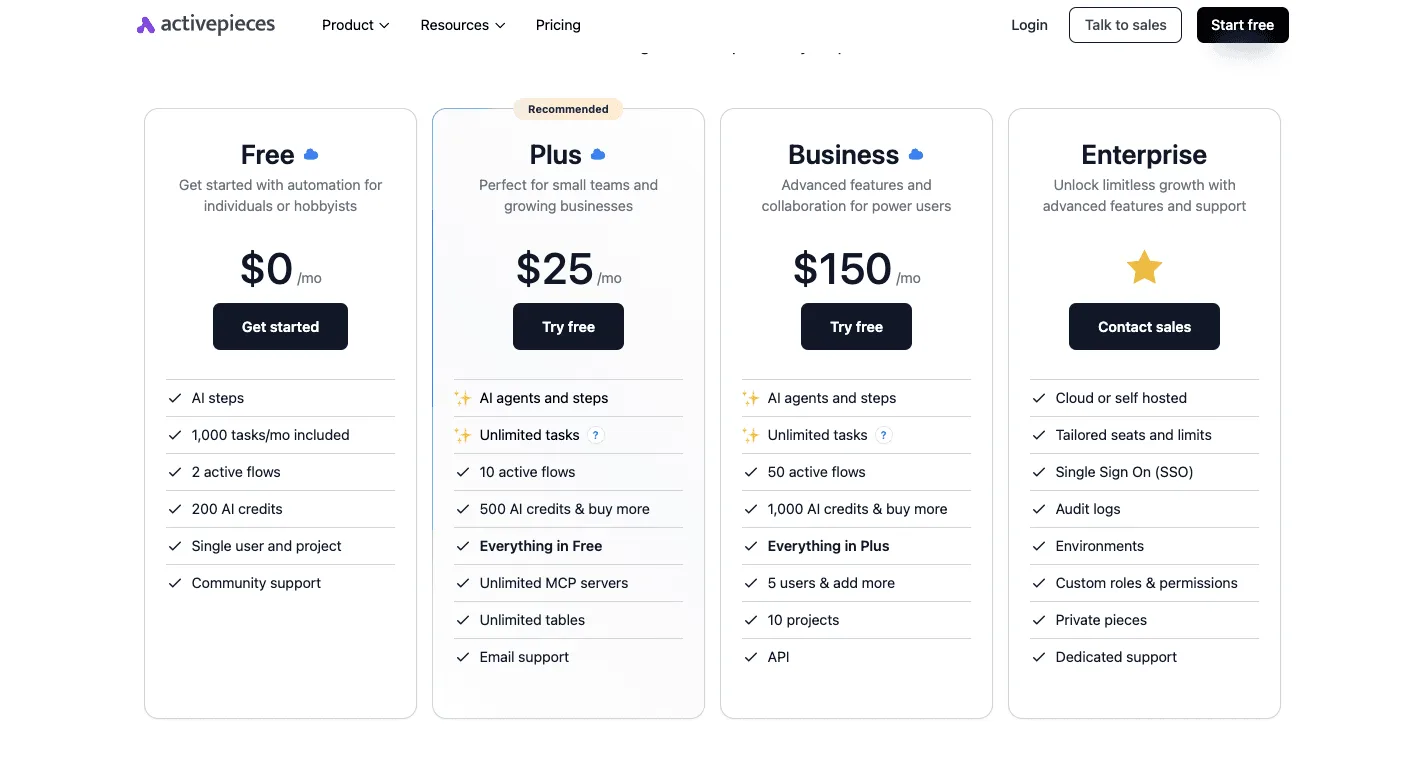
Activepieces lists Plus at $20 a month and Team at $200 a month on its pricing page, with Ultimate handled through https://www.activepieces.com/sales, which means prospective customers cannot evaluate all three tiers without a sales conversation.
Frequently asked questions
Is Zapier SOC 2 certified?
Treat Zapier's SOC 2 attestation as a claim until you have read the report itself, though its trust pages state that it holds one.
SOC 2 is an auditor's report, not a certificate, and it covers the vendor's own systems, not the workflows you build on them.
A clean report doesn't tell you whether your lawful basis is documented or whether a workflow is copying special-category data into a tool it should never reach. Request the current report through Zapier's trust channel and read the scope and exceptions sections.
Can I keep Zapier data in the EU?
Don't assume you can; confirm on Zapier's own security and privacy pages which regions your plan processes data in.
If processing happens outside the EU, the question becomes whether your DPA includes a valid transfer mechanism, such as standard contractual clauses, and whether you have recorded a transfer assessment.
Avoid the workflow that quietly moves EU personal data to a third country because nobody checked where the step ran. Each connected app is a separate transfer, so the answer for Zapier doesn't cover the apps on either side of it.
How do I delete personal data from Zapier history?
Delete in every place the data landed, not only in Zapier. Task history and logs hold the payloads your workflows passed through, so set the retention period in your account settings and check what Zapier's documentation says about removing individual records.
Then trace each workflow's destination apps, because a record erased from Zapier's history still exists in the spreadsheet, CRM or inbox it was written to. A data subject's erasure request is only complete once all those copies are gone.

What should I ask in a security review?
Before a workflow touches personal data, a reviewer should be able to tick off everything on the checklist below. Anything left unticked means the paperwork is incomplete, whatever the vendor publishes.
- DPA on file and signed
- Lawful basis recorded per workflow
- Subprocessor list reviewed
- Retention period set
- SSO enforced
- Transfers checked
Once these are settled, ask the vendor for the written evidence behind each item.
Activepieces' free plan costs $0 with 1,000 credits a month, unlimited flows and up to 5 users, so you can test the answers against a real workflow before buying; Ultimate terms come through https://www.activepieces.com/sales.