n8n SOC 2: What It Covers and Which Plans (2026)

Oct 18, 202614 min read
As of 18 October 2026, n8n publicly describes its hosted cloud service as SOC 2 audited.
I couldn't confirm the report type or which plan it extends to from n8n's own pages, and, as with other Activepieces-style automation tools you might compare it against, the public claim alone tells you little. Treat both as open until you hold the report.
To see where plan gating would show up, go to the pricing page; to request the report, go to n8n's trust page.
In a SOC 2 audit, an outside firm tests a vendor's stated controls against criteria for security and related areas. It produces a report, not a certificate. The report is the artifact you read, and the badge is only a pointer to it.

n8n SOC 2 status explained
Type I versus Type II, and the report period
Only Type II tells you the controls kept working. A Type I report describes whether controls were suitably designed on a single date, while a Type II report tests whether they operated across a stated window.
Only Type II tells you the controls kept working.
Then read the dates on the cover: a window that ended long ago means the controls you are relying on were last tested before the vendor's current setup existed.
Which n8n product the report describes
For n8n, the audit covers the system the vendor describes in its own scope section, which is the hosted cloud service. A self-hosted install runs on your infrastructure, under your controls, so the vendor's report doesn't vouch for it.
Apply the same boundary to the self-hosted build itself, because a stripped self-hosted edition is where vendors usually hold the controls back.
Activepieces doesn't sell its air-gapped customers a smaller product: the enterprise feature list of single sign-on, SCIM provisioning, custom roles, audit logs, release management and secret managers reads identically in the air-gapped docs and for the managed cloud in an EU or US region, the deployment that SOC 2 Type II describes.
Regulated and public-sector teams run that air-gapped edition in production today. The report's scope changes between the two, but the controls don't.
Everything below works on Activepieces' free plan. Start without code or a credit card.
n8n security requirements by plan and price
Where n8n's pricing page names no plan or price for a requirement, the table below says so. Read it as of 18 October 2026: the cells filled in are the ones the page supports.
| Requirement | What n8n states | Plan | Price (€) |
|---|---|---|---|
| SOC 2 report access | not stated on the page | not stated on the page | not stated on the page |
| SSO | not stated on the page | not stated on the page | not stated on the page |
| RBAC | not stated on the page | not stated on the page | not stated on the page |
| Audit logs | not stated on the page | not stated on the page | not stated on the page |
| EU data residency | not stated on the page | not stated on the page | not stated on the page |
| Self-hosting | Self-hosted Free, Business and Enterprise tiers are listed | Self-hosted | not stated on the page |

Take every blank to n8n's sales team as a question, because a feature the page doesn't name can't be put in a procurement file.
At 20 € per month, Cloud Starter scores one of four security features in the pricing matrix, so it can't satisfy a checklist with several items.
Pro is 50 € per month, and Business is 667 € per month, about thirteen times Pro.
If you need more than one of those features, Cloud Enterprise is the plan that scores all four, and you are in a quoted-price conversation, because the page gives no euro figure for it.
Run the code yourself on the Free self-hosted tier and you score zero of four, so self-hosting buys data control, not security features.

Self-hosted Business scores two of four, and Self-hosted Enterprise scores all four.
SOC 2 report scope and limits
Your install's configuration isn't included in the report. Only the systems the vendor put in scope are covered, tested against the criteria it chose, over a stated audit period.
Hosted service versus self-hosted install
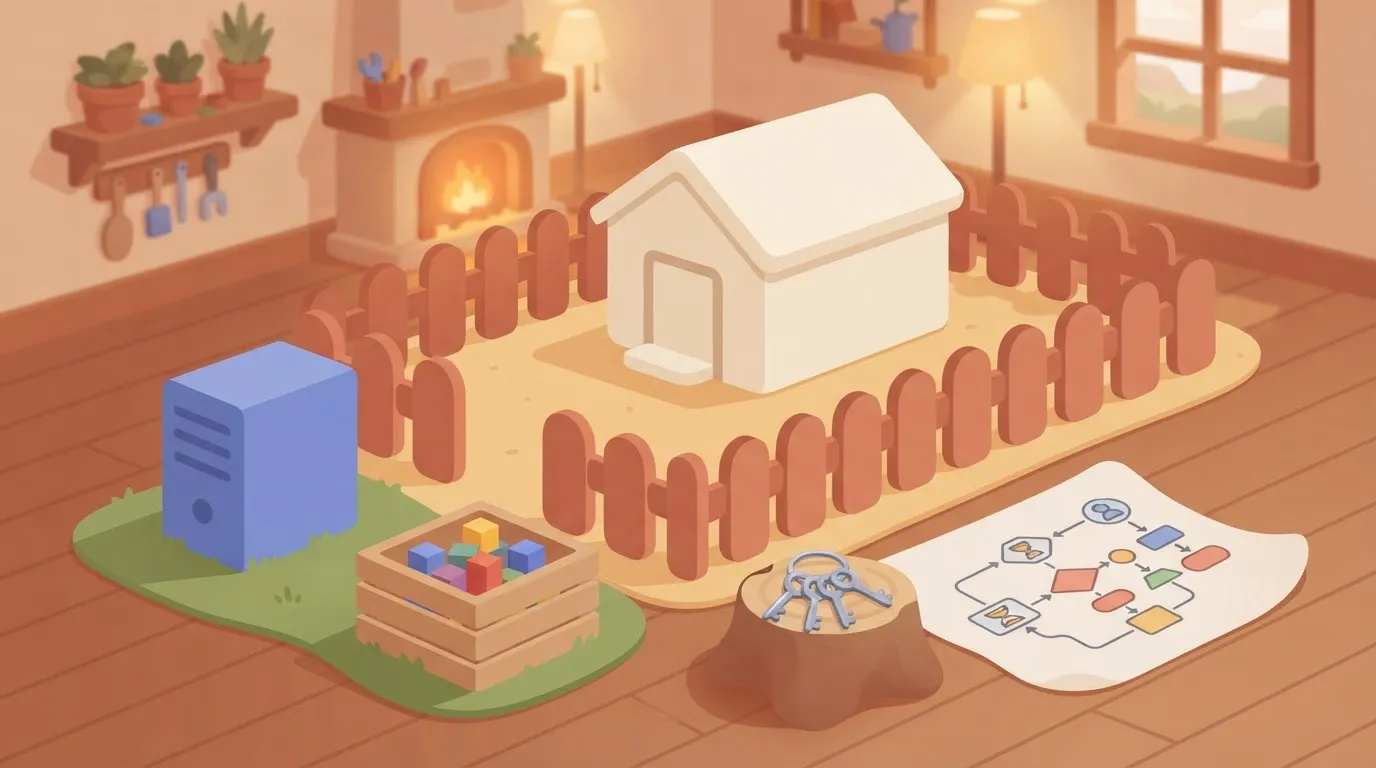
The auditor tests the vendor's hosted service: its servers, its staff access, its change process. A server you run from the vendor's compose file's your infrastructure, so none of those tested controls transfer to it. Patching, backups and network exposure are yours to evidence.
In the boundary diagram below, the audited hosted service sits inside a solid line, with the self-hosted server, community nodes, stored credentials and workflow design outside it, marked out of scope.
Only security is a mandatory trust criterion. Availability, confidentiality, processing integrity and privacy are optional, so a report that omits confidentiality says nothing about how customer data is protected from disclosure.
Check which ones the vendor selected. Then read the exclusions, since the auditor never tested a carved-out component.
Subprocessors and the n8n SOC 2 report
When a report treats subprocessors, such as the cloud host, with the carve-out method, it describes them but doesn't test them. Their controls are then someone else's report, which you must request separately.

30% of breaches involved a third party, according to the Verizon 2025 breach report, as summarised by ASIS Security Management.

Nearly one breach in three runs through a vendor's supply chain, so a clean report on the primary vendor leaves a large share of your risk unexamined. List the subprocessors and ask for each one's attestation.
Mistakes buyers make with a SOC 2 claim
Six misreadings account for most of the damage. Run the table's right-hand column against the vendor's actual documents before signing.
Mistaking a badge for a report
Until you hold the report itself, a logo on a pricing page proves nothing, because SOC 2 is an attestation issued by an auditor, not a certification.
Three mistakes live here: treating the badge as certification, accepting a Type I (design of controls at one date) as a Type II (controls operating over a period), and ignoring the period.
Assuming self-hosted inherits the audit
When you run the software from your own compose file or Helm chart, your servers, your patching and your network sit outside the audited boundary. The report describes the vendor's hosted service, so the vendor's controls don't travel with the code.
Read the system description for what's in scope, then treat your own deployment as something you must evidence yourself.
Treating SOC 2 as HIPAA or GDPR cover
Because SOC 2 tests controls against criteria the vendor chose, it doesn't grant a Business Associate Agreement or satisfy data-residency and processor obligations. Ask for those documents separately.
Also check plan gating: SSO and audit logs often sit on higher tiers, so the secure product you reviewed may not be the one you pay for.
| Mistake | Consequence | Check to run |
|---|---|---|
| Calling SOC 2 a certification | You accept a logo with no auditor's opinion behind it | Request the full report under NDA |
| Type I treated as Type II | Controls were never tested in operation | Confirm the report type on its cover |
| Ignoring the period | Coverage may have lapsed or predate major changes | Compare the period dates to today and to your term |
| Self-host inherits report | Your deployment is unaudited | Read the scope; list what you must control |
| SOC 2 equals HIPAA/GDPR | Missing BAA or processor terms | Ask for those documents by name |
| SSO/logs on higher plans | Required controls are unavailable on your tier | Map each requirement to a plan in writing |
Easier to see it running than to read about it: set it up free, no card.
Activepieces controls against the same checklist
Six controls answer the written-answers list at Activepieces. They're SOC 2 Type II, SSO and SCIM, custom RBAC, audit logs, a managed cloud in an EU or US region, and self-host with air-gap.
Which one applies depends on where your workflows run, and that decides what a report can vouch for.
Managed cloud in an EU or US region
On the managed cloud, Activepieces runs the service and you pick an EU or US region. That's the deployment the SOC 2 Type II report is about.
So ask for the report itself and check its scope and period against the hosted service you'd actually use.
For residency, region choice matters: your workflow data stays in the region you selected, which is the answer a GDPR-minded reviewer is looking for. It doesn't make your own flows or third-party connections part of the audit.
Self-host and air-gap
A self-hosted install runs on your infrastructure, so the vendor's report doesn't cover it. Treat that as the point rather than a gap: you can read the compose file and the source tree, and you decide what leaves the network.
With an air-gapped deployment, workflow data never crosses your boundary, so a regulated team can keep data in its own environment. We make no HIPAA, BAA or ISO claim here. For a self-hosted install, your own controls are the ones that get audited.
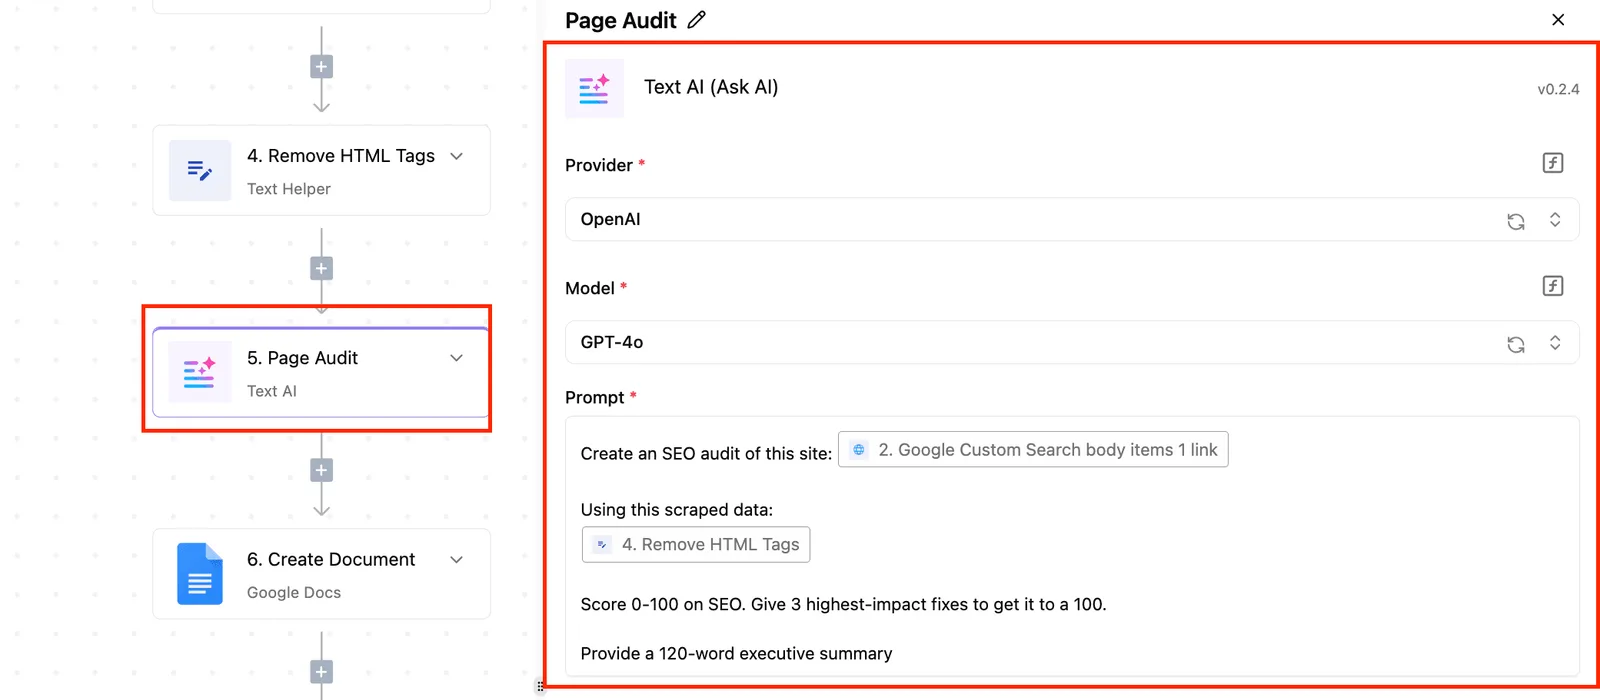
These are the controls a reviewer will test against a live account, not a PDF:
- SSO and SCIM, so sign-in goes through your identity provider and leavers are deprovisioned from there rather than by hand.
- Custom RBAC, so a contractor gets only the flows and connections their job needs.
- Audit logs, so you can show who changed or ran what when asked.
Confirm which tier carries each one.
Activepieces Cloud lists Plus at $20 a month and Team at $200 a month, with Ultimate quoted through https://www.activepieces.com/sales, and in the repository the enterprise directories (packages/ee/) sit under a separate commercial licence from the MIT-licensed core, so anyone deploying in production cannot rely solely on the open-source code.
Questions to ask in an automation security review
Put the same eight questions to every vendor in writing, and ask for the answers as documents you can read rather than a badge on a trust page.
- Which report do you hold, Type I or Type II, and what dates does the observation period cover? A Type I describes controls at a single point in time, so it says nothing about whether they kept working afterward. A period that ended long ago leaves you guessing about the months since.
- What's in scope, and what is excluded? Ask for the system description, and check whether it names the hosted service only, or also the self-hosted install and the workflows you build on it.
- Which plan unlocks each control you need: single sign-on, role-based access, audit logs, network isolation? A control that exists on the enterprise tier doesn't protect a team on a lower one.
- Where is data stored and processed, and can you choose the region?
- Who are the subprocessors, and how are you told when the list changes?
- How are the credentials for connected apps stored, encrypted, and accessed by vendor staff?
- How long are execution logs kept, and can you export or shorten that window? Retained run data may hold the very records you were trying to protect.
- What are the breach notice terms, in the contract, including who is told, how fast, and in what form?
Once the answers are in hand, compare them against the report itself, not the summary.
Activepieces Cloud's free plan costs $0 and includes unlimited flows and up to 5 users, so you can run a workflow on a live account while the report is in transit; security documents and enterprise pricing go through https://www.activepieces.com/sales.
Monday plan for closing the security review
Request the security documents through sales first, then work these six steps in order, because each one narrows what the next has to prove:
- Write the requirement list: every control you must meet, named as your auditor names it, such as SSO, audit logs or data residency.
- Request each vendor's full report under NDA, not the badge or the summary letter.
- Check the report period and scope: which dates the audit window covers, and whether the system description names the hosted service you'll actually use.
- Map each control to the plan that includes it, and write down that plan's price.
- Decide cloud versus self-host for each workload.
- Record verification dates: who confirmed what, from which document, on what day.
Steps four and five are where most reviews stall, so the three paragraphs below cover them.
Read the plan comparison page line by line against your requirement list, and copy what it says into your notes. A control listed on a lower tier is the one you can price today.
Anything marked "contact us" isn't yet a fact, so leave it unchecked until the vendor puts it in writing.
If your list needs SCIM provisioning, custom roles, audit log export or a chosen data region, expect to pay for the top tier, because those controls are often sold only there.
The real price is then the enterprise quote, not the sticker plan. Get that quote with the control named in it, so a later renewal can't quietly drop it.
Because a cloud report covers the vendor's hosted service, a self-hosted install sits outside it. Your own team then owns patching, access control and logging, and you'll answer for them in your own audit. In exchange, data stays inside your network.
Frequently asked questions
Is n8n SOC 2 compliant if I self-host it?
Not by inheritance, no. A SOC 2 report covers the vendor's hosted service, so a self-hosted install of n8n sits outside it. The servers, patching, secrets storage and access controls become yours to evidence.
Read your own compose file and image sources, record the version you reviewed, and bring that install into your own audit scope.
How do I get n8n's SOC 2 report?
Ask n8n through its trust center or security contact, or through sales if the report is gated. Vendors commonly release the full report only under an NDA, and access can depend on plan.

Once you have it, read three things: the system description (what's in scope), the report period (the dates it covers), and any exceptions the auditor noted. A badge on a pricing page shows none of these.
Does SOC 2 mean n8n is GDPR compliant?
No. SOC 2 is an audit of security controls against the Trust Services Criteria. GDPR is a law with its own obligations: a data processing agreement, a lawful basis for processing, a list of subprocessors, and rules on transferring data out of the EU.
A clean SOC 2 report supports a GDPR review but doesn't replace it. Request the DPA and the subprocessor list separately, and confirm in writing where your workflow data is stored.
How often should I recheck a vendor's SOC 2 status?
Recheck whenever a new report is issued and before every contract renewal. A report describes a past period, so it says nothing about what changed after the period closed.
After a vendor incident, a change of hosting provider, or a plan change that moves you onto different infrastructure, recheck as well. At each check, compare the new scope and period against the previous report and note any difference in the ticket.